GV

GeezerVison

The World Wide Web, restored to 800 pixels of glory.

Home|About|Gaming cabinet|Archives|How it works|Starter sites

On this site

  • Sign in
  • ActionsCI/CD and automation
  • CodespacesCloud development environments
  • All Features
  • Documentation
  • Training
  • Certifications
  • Build with Copilot
  • Customize Copilot
  • Integrations
  • Trending repos
  • GitHub Sponsors
  • Developer articles
  • Enterprises

This view

  • Original page
  • New address

GeezerVison is showing github.com — fibratus/rules at master · rabbitstack/fibratus

Expand file tree

/

rules

/
Copy path

Directory actions

More options

More options

Directory actions

More options

More options

Latest commit


History

History
History
/

rules

/
Copy path

Folders and files

NameName
Last commit message
Last commit date

parent directory

..
linux
linux
 
 
macros
macros
 
 
README.md
README.md
 
 
credentail_access_file_access_to_sam_database.yml
 
 
credential_access_credential_manager_access_via_known_tools.yml
 
 
credential_access_lsass_access_from_unsigned_executable.yml
 
 
credential_access_lsass_handle_leak_via_seclogon.yml
 
 
credential_access_lsass_memory_dump_preparation_via_silent_process_exit.yml
 
 
credential_access_lsass_memory_dump_via_minidumpwritedump.yml
 
 
credential_access_lsass_memory_dump_via_wer.yml
 
 
credential_access_lsass_process_clone_creation_via_reflection.yml
 
 
credential_access_potential_lsass_memory_dump.yml
 
 
credential_access_potential_ntlm_hash_leak_via_ms_photos.yml
 
 
credential_access_potential_ntlm_hash_leak_via_shortcut_file.yml
 
 
credential_access_registry_access_to_sam_database.yml
 
 
credential_access_remote_thread_creation_into_lsass.yml
 
 
credential_access_sensitive_registry_hive_dump.yml
 
 
credential_access_suspicious_access_to_active_directory_domain_database.yml
 
 
credential_access_suspicious_access_to_unattended_panther_files.yml
 
 
credential_access_suspicious_access_to_windows_dpapi_master_keys.yml
 
 
credential_access_suspicious_access_to_windows_manager_files.yml
 
 
credential_access_suspicious_access_to_windows_vault_files.yml
 
 
credential_access_suspicious_lsa_secrets_registry_access.yml
 
 
credential_access_suspicious_lsass_process_access.yml
 
 
credential_access_suspicious_security_package_loaded_by_lsass.yml
 
 
credential_access_suspicious_vault_client_dll_load.yml
 
 
credential_access_unusual_access_to_ssh_keys.yml
 
 
credential_access_unusual_access_to_web_browser_credential_stores.yml
 
 
credential_access_unusual_access_to_windows_credential_history.yml
 
 
defense_evasion_activation_context_memory_section_hijacking.yml
 
 
defense_evasion_activity_from_unhooked_ntdll_module.yml
 
 
defense_evasion_appdomain_manager_injection_via_clr_search_order_hijacking.yml
 
 
defense_evasion_bindflt_dll_loaded_by_an_unusual_process.yml
 
 
defense_evasion_cldapi_dll_loaded_by_an_unusual_process.yml
 
 
defense_evasion_clear_eventlog.yml
 
 
defense_evasion_direct_disk_device_access.yml
 
 
defense_evasion_dll_loaded_via_apc_queue.yml
 
 
defense_evasion_dll_loaded_via_callback_function.yml
 
 
defense_evasion_dll_loaded_via_ldrpkernel32_overwrite.yml
 
 
defense_evasion_dll_sideloading_via_copied_binary.yml
 
 
defense_evasion_dll_sideloading_via_microsoft_office_dropped_file.yml
 
 
defense_evasion_dotnet_assembly_loaded_by_unmanaged_process.yml
 
 
defense_evasion_hidden_registry_key_creation.yml
 
 
defense_evasion_image_load_via_ntfs_transaction.yml
 
 
defense_evasion_potential_injection_via_dotnet_debugging.yml
 
 
defense_evasion_potential_ntdll_unhooking_via_file_mapping.yml
 
 
defense_evasion_potential_operation_evasion_via_direct_syscall.yml
 
 
defense_evasion_potential_process_creation_via_shellcode.yml
 
 
defense_evasion_potential_process_injection_via_tainted_memory_section.yml
 
 
defense_evasion_potential_shellcode_execution_via_etw_logger_thread.yml
 
 
defense_evasion_potential_shellcode_injection_via_windows_debugging_api.yml
 
 
defense_evasion_potential_thread_execution_hijacking.yml
 
 
defense_evasion_process_creation_from_stomped_module.yml
 
 
defense_evasion_process_creation_via_direct_syscall.yml
 
 
defense_evasion_process_creation_via_ntfs_transaction.yml
 
 
defense_evasion_process_execution_from_hollowed_memory_section.yml
 
 
defense_evasion_process_execution_from_remote_memory_section.yml
 
 
defense_evasion_process_execution_from_self_deleting_binary.yml
 
 
defense_evasion_process_spawned_from_unusual_directory.yml
 
 
defense_evasion_process_spawned_via_remote_thread.yml
 
 
defense_evasion_regsvr32_scriptlet_execution.yml
 
 
defense_evasion_suspicious_access_to_the_hosts_file.yml
 
 
defense_evasion_suspicious_activity_from_reflected_process.yml
 
 
defense_evasion_suspicious_child_spawned_via_reflected_process.yml
 
 
defense_evasion_suspicious_dll_loaded_via_memory_section_mapping.yml
 
 
defense_evasion_suspicious_html_application_script_execution.yml
 
 
defense_evasion_suspicious_object_symbolic_link_creation.yml
 
 
defense_evasion_suspicious_protected_process_execution.yml
 
 
defense_evasion_suspicious_virtual_path_redirection_via_bind_filter.yml
 
 
defense_evasion_suspicious_windows_defender_exclusions_registry_modification.yml
 
 
defense_evasion_suspicious_xsl_script_execution.yml
 
 
defense_evasion_system_binary_proxy_execution_via_rundll32.yml
 
 
defense_evasion_thread_context_manipulation_from_exception_handler.yml
 
 
defense_evasion_thread_context_set_from_unbacked_memory.yml
 
 
defense_evasion_unsigned_dll_injection_via_remote_thread.yml
 
 
defense_evasion_untrusted_dll_loaded_from_unusual_directory.yml
 
 
defense_evasion_windows_defender_driver_unloading.yml
 
 
defense_evasion_windows_defender_protection_tampering_via_registry.yml
 
 
execution_embedded_executable_file_run_via_shortcut.yml
 
 
execution_embedded_script_execution_via_shortcut_file.yml
 
 
execution_process_execution_from_compressed_file_via_explorer.yml
 
 
execution_suspicious_mshta_execution_via_html_smuggling.yml
 
 
execution_suspicious_process_execution_from_archive_via_shortcut_file.yml
 
 
initial_access_clickfix_phishing_via_browser_dialog_box.yml
 
 
initial_access_executable_file_creation_from_macro_enabled_microsoft_office_document.yml
 
 
initial_access_execution_via_microsoft_office_process.yml
 
 
initial_access_macro_execution_via_script_interpreter.yml
 
 
initial_access_microsoft_office_file_execution_via_script_interpreter.yml
 
 
initial_access_microsoft_office_file_execution_via_wmi.yml
 
 
initial_access_potential_clickfix_infection_chain.yml
 
 
initial_access_process_spawned_from_macro_enabled_microsoft_office_document.yml
 
 
initial_access_suspicious_dll_loaded_by_microsoft_office_process.yml
 
 
initial_access_suspicious_execution_via_wmi_from_microsoft_office_process.yml
 
 
initial_access_suspicious_file_delivery_via_html_smuggling.yml
 
 
initial_access_suspicious_microsoft_office_embedded_object.yml
 
 
lateral_movement_dll_loading_of_a_file_transferred_over_smb.yml
 
 
lateral_movement_execution_of_a_file_transferred_over_smb.yml
 
 
persistence_executable_file_dropped_by_unsigned_service_dll.yml
 
 
persistence_hidden_local_account_creation.yml
 
 
persistence_network_connection_via_startup_folder_executable_or_script.yml


README.md

Outline

Detection Rules

Email rule alert

This directory contains a catalog of detection rules mapped to MITRE ATT&CK framework. The goal is to provide a direct mapping of tactics, techniques, and sub-techniques for each rule. The following sections introduce the general structure, design guidelines, and best practices to keep in mind when creating new rules.

Structure

Detection rules are organized in yaml files. Rules can live in different directories and there is no strict naming convention. However, the recommended practice is to follow the tactic_name_rule_name.yml naming nomenclature. By default, all rules reside within the rules directory of this repository.

The CLI provides a command to create a new rule from the template. For example, if you want to create the Potential Process Doppelganging rule that belongs to the Defense Evasion MITRE tactic, you would use the following command.

$ fibratus rules create "Potential Process Doppelganging Injection" -t TA0005

The -t flag specifies the MITRE tactic id. The end result is the defense_evasion_potential_process_doppelganging_injection.yml file with the most required attributes such as rule identifier, name, and the minimum engine version, filled out automatically.

Guidelines

Read the docs

This should be your starting point. Before trying to write new rules, explore the docs to learn about operators, functions, filter fields reference.

Stick to naming nomenclature

It is highly recommended to name the rule files after the pattern explained in the above section. This facilitates the organization and searching through the detection rules catalog and fosters standardization.

Include descriptions and labels

Rules should have a meaningful description. For example, Potential process injection via tainted memory section.

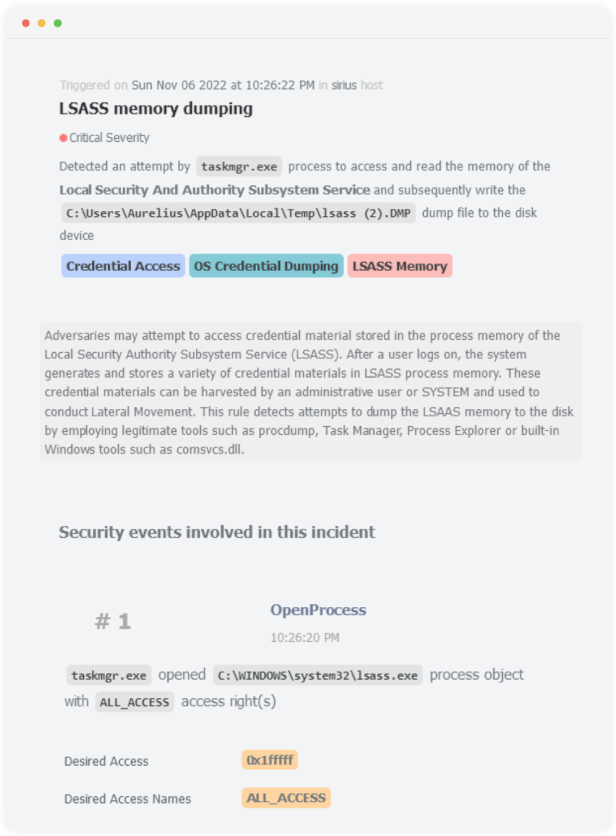
Additionally, there should exist labels attached to every rule describing the MITRE tactic, technique, and sub-technique. This information is used when rendering email rule alert templates as depicted in the image above.

Rules should have a narrowed event scope

If a rule is declared without the scoped event conditions, you'll get a warning message in Fibratus logs informing you about unwanted side effects. This always lead to the rule being utterly discarded by the engine!

Pay attention to the condition arrangement

As highlighted in the previous paragraph, all rules should have the event type condition. Additionally, condition arrangement may have important runtime performance impact because the rule engine can lazily evaluate binary expressions that comprise a rule. In general, costly evaluations or functions such as get_reg_value should go last to make sure they are evaluated after all other expressions have been visited.

Prefer macros over raw conditions

Fibratus comes with a macros library to promote the reusability and modularization of rule conditions and lists. Before trying to spell out a raw rule condition, explore the library to check if there's already a macro you can pull into the rule. For example, detecting file accesses could be accomplished by declaring the evt.name = 'CreateFile' and file.operation = 'open' expression. However, the macro library comes with the open_file macro that you can directly call in any rule. If you can't encounter a particular macro in the library, please consider creating it. Future detection engineers and rule writers could profit from those macros.

Formatting styles

Pay attention to rule condition/action formatting style. If the rule consists of multiple or large expressions, it is desirable to split each spanning expression on a new line. This notably improves readability and prevents formatting inconsistencies.

You are visitor 01402520 — GeezerVison does not store the pages you look up.
Best viewed with Netscape Navigator 4.7 or Internet Explorer 6 at 800×600. No cookies required.