GeezerVisonThe World Wide Web, restored to 800 pixels of glory. |
| Home|About|Gaming cabinet|Archives|How it works|Starter sites |
GeezerVison is showing osv.dev — OSV - Open Source Vulnerabilities A distributed vulnerability database for Open SourceAn open, precise, and distributed approach to producing and consuming vulnerability information for open source. Ecosystems
OSV schemaAll advisories in this database use the OpenSSF OSV format, which was developed in collaboration with open source communities. The OSV schema provides a human and machine readable data format to describe vulnerabilities in a way that precisely maps to open source package versions or commit hashes. Data sourcesThis infrastructure serves as an aggregator of vulnerability databases that have adopted the OSV schema, including GitHub Security Advisories, PyPA, RustSec, and Global Security Database, and more. Use the APIAn easy-to-use API is available to query for all known vulnerabilities by either a commit hash, or a package version. Query by commit hashcurl -d \
'{"commit": "6879efc2c1596d11a6a6ad296f80063b558d5e0f"}' \
"https://api.osv.dev/v1/query"
Query by version numbercurl -d \
'{"version": "2.4.1",
"package": {"name": "jinja2", "ecosystem": "PyPI"}}' \
"https://api.osv.dev/v1/query"
Vulnerability ScannerInstall OSV‑Scannergo install github.com/google/osv-scanner/v2/cmd/osv-scanner@v2
Scan SBOM or Lockfilesosv-scanner --sbom=cycloned-or-spdx-sbom.json
osv-scanner --lockfile=package-lock.json
Scan directory recursivelyosv-scanner -r path/to/your/project
Remediation ToolsGuided Remediation (basic)osv-scanner fix --non-interactive --strategy=in-place -L path/to/package-lock.json
osv-scanner fix --non-interactive --strategy=relock -M path/to/package.json -L path/to/package-lock.json
Guided Remediation (interactive)osv-scanner fix -M path/to/package.json -L path/to/package-lock.json
Container Image ScanningYou can use OSV-Scanner to scan your container images for known vulnerabilities. Scan container imageosv-scanner scan image --serve alpine:3.12
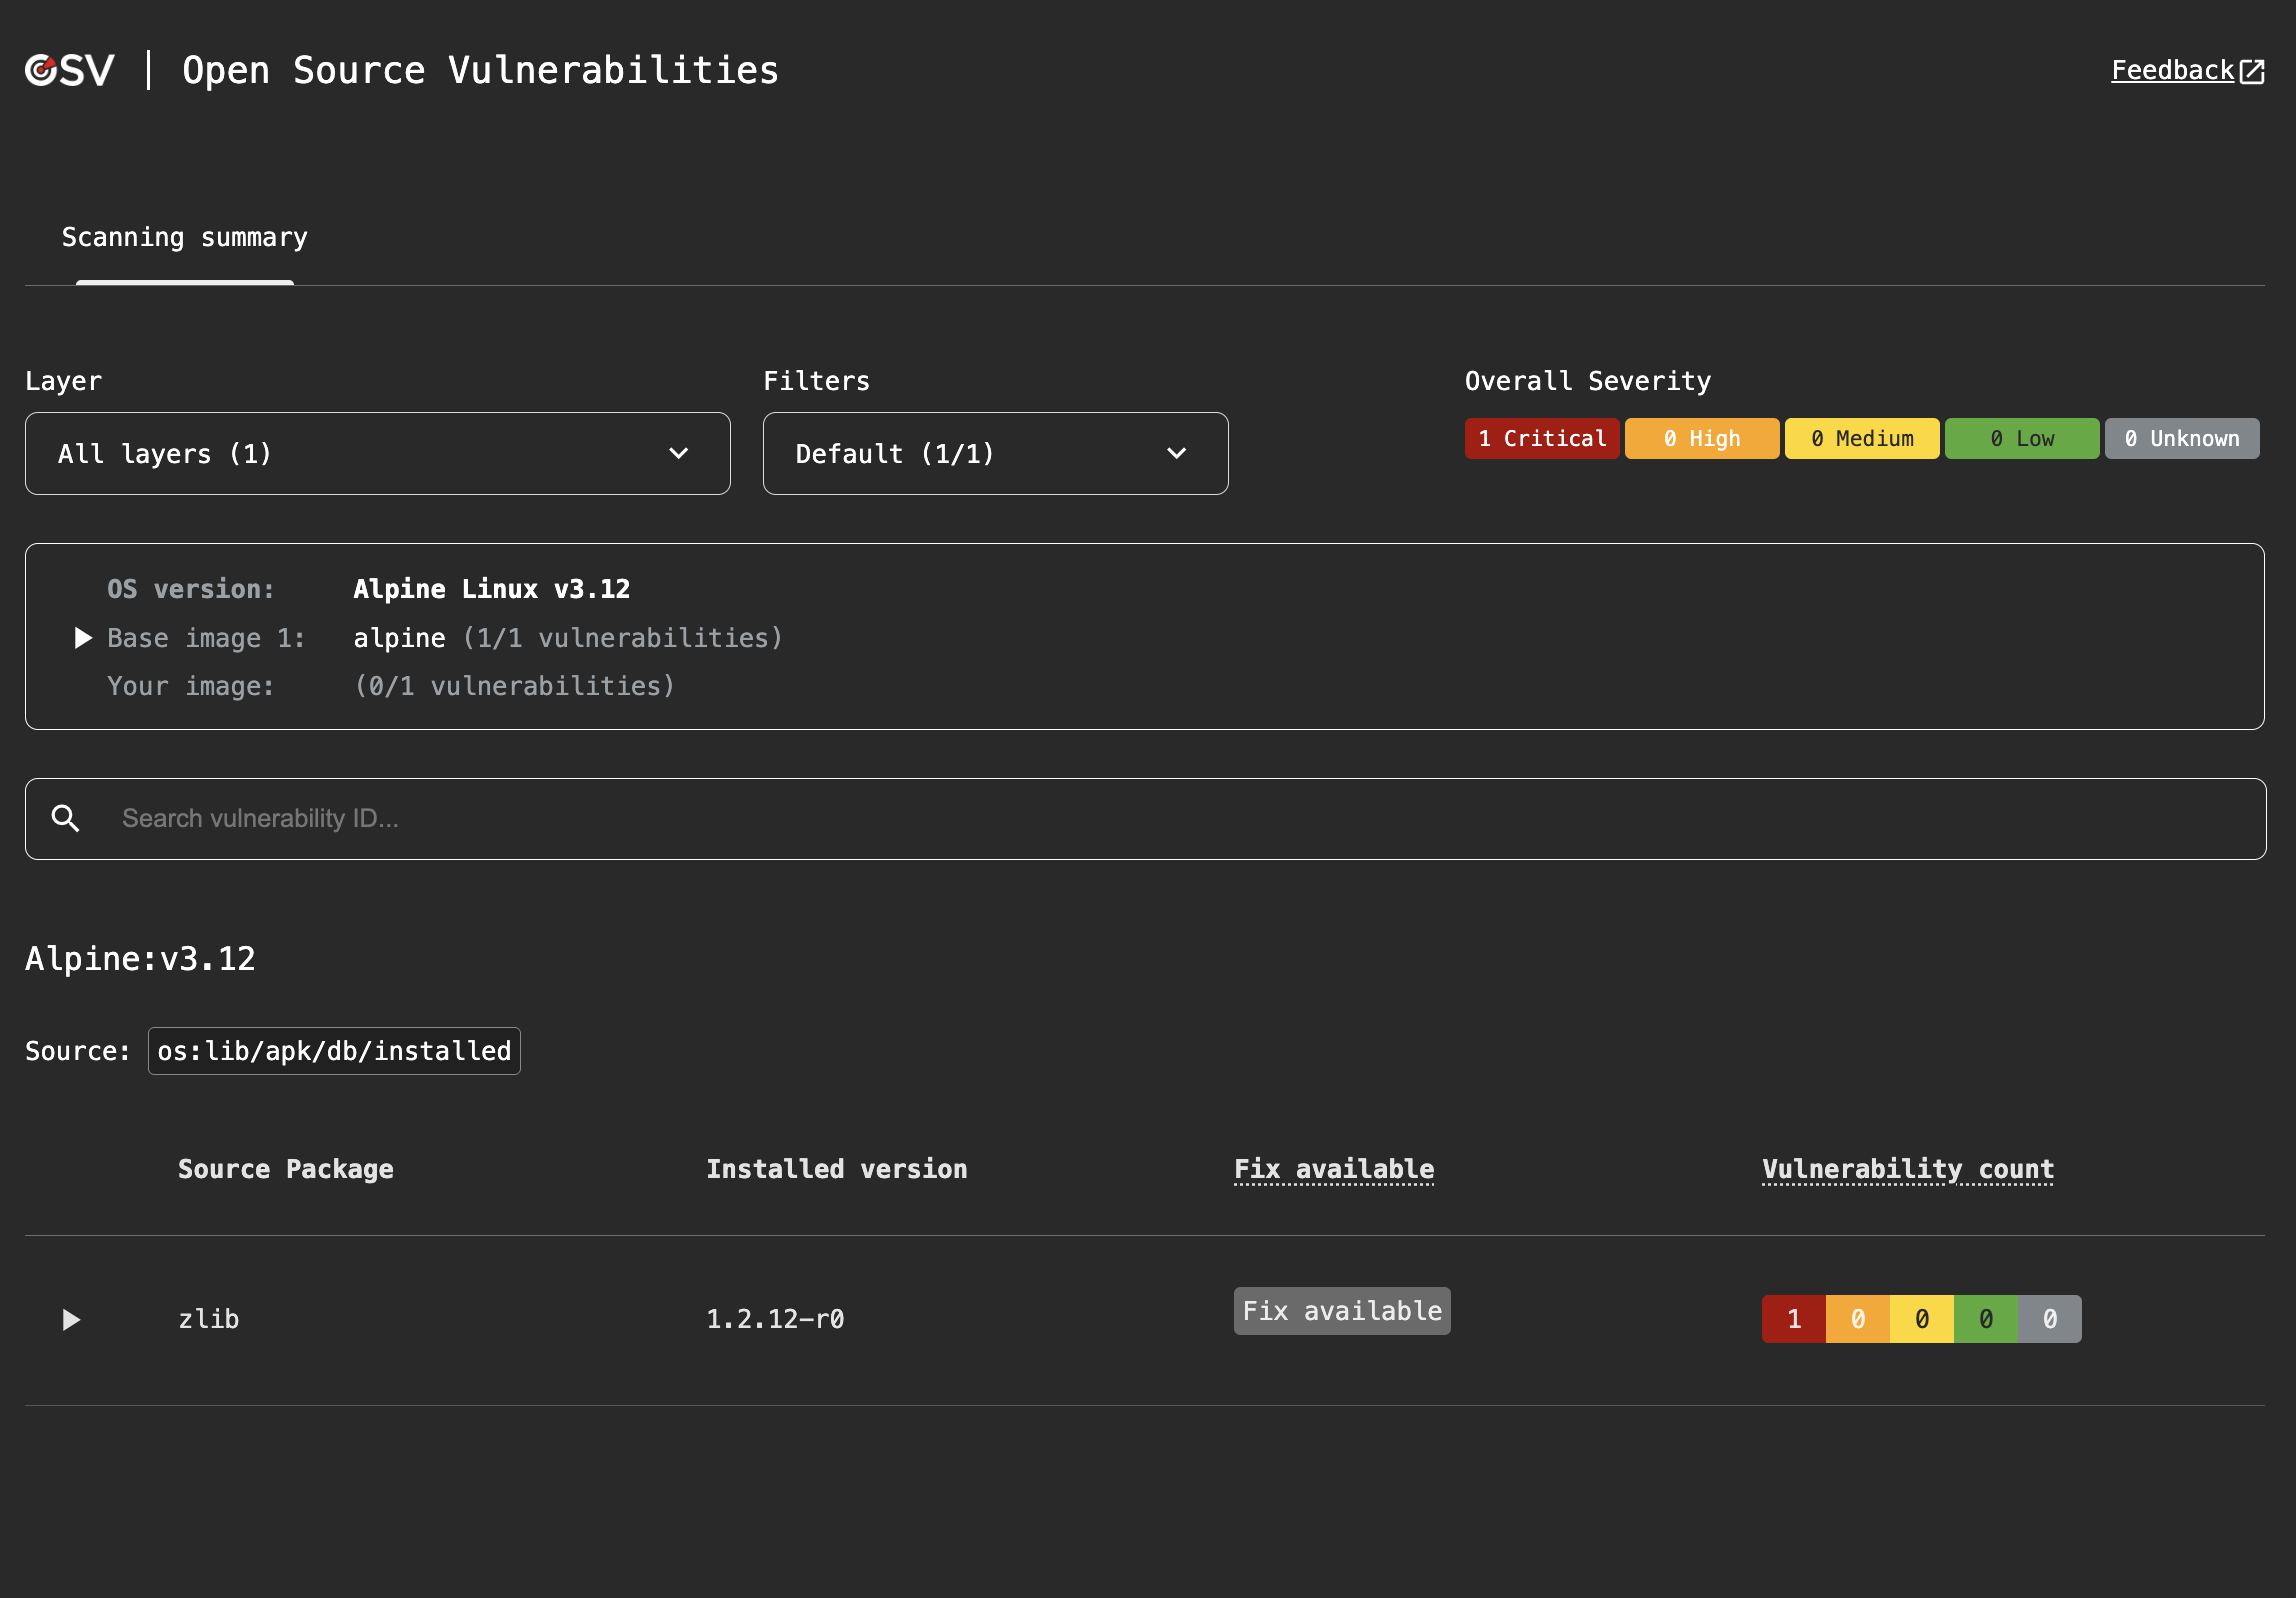
GitHub WorkflowsOSV-Scanner also provides reusable GitHub workflows that can be easily integrated into CI/CD pipelines to provide continuous vulnerability scanning coverage. This can scan newly added dependencies in pull requests for introduced vulnerabilities, as well as perform regular vulnerability scans for the entire project. 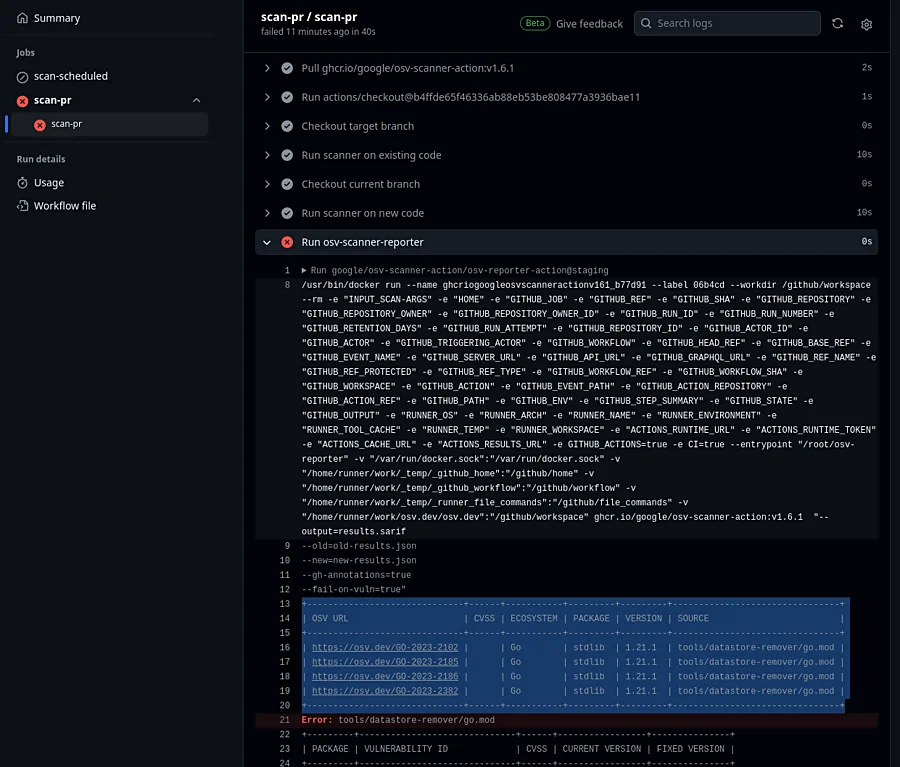 Open sourceThis project is open source. If you have any ideas or questions, please feel free to reach out by creating an issue! |
| You are visitor 01402503 — GeezerVison does not store the pages you look up. Best viewed with Netscape Navigator 4.7 or Internet Explorer 6 at 800×600. No cookies required. |