GeezerVisonThe World Wide Web, restored to 800 pixels of glory. | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Home|About|Gaming cabinet|Archives|How it works|Starter sites | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
GeezerVison is showing docs.stackstorm.com — Authentication — StackStorm 3.9.0 documentation AuthenticationHint Just need the default password? Try username Need to change the password? Run: Something more complex? Read on to learn about StackStorm authentication. StackStorm includes an auth service that is responsible for handling user authentication and generating time-limited access tokens. When authentication is enabled (the default), those access tokens are used to authenticate against the StackStorm REST APIs. 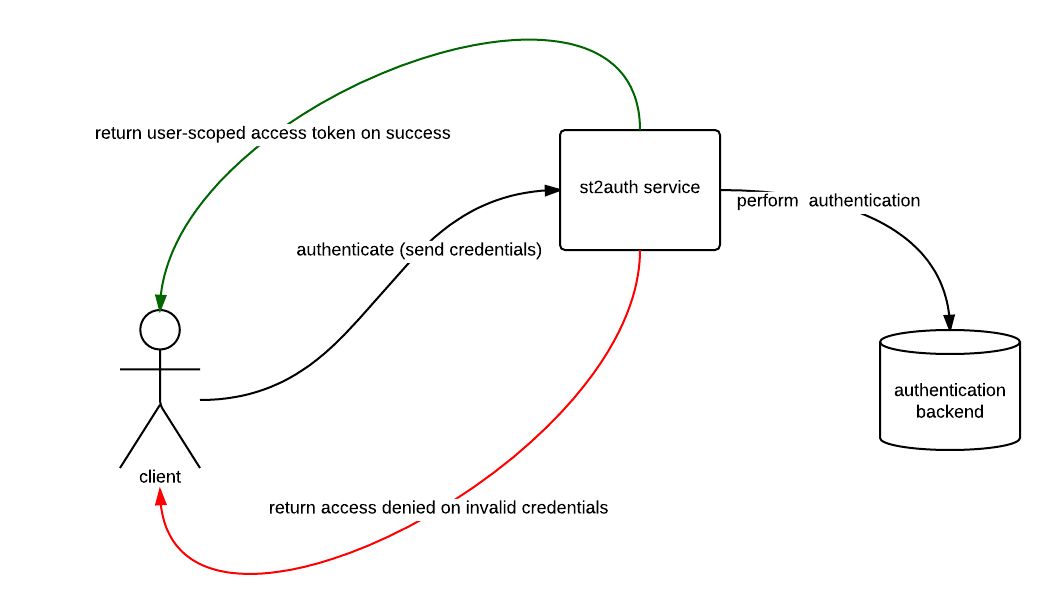
Configuring the ServiceBy default, the StackStorm configuration file is located at We recommend that the service be configured to listen on https (
If you make any changes, you must restart StackStorm: $ sudo st2ctl restart Standalone Auth ModeStandalone mode is the default auth mode where external users authenticate directly with
StackStorm. Under the hood the Proxy Auth ModeProxy mode can be used when there is a service (proxy) that sits in front of StackStorm
that performs user authentication (ex: load balancer, apache, nginx, etc). When
the frontend service authenticates a user, it will need to make an API call
The request will return an auth token that authenticated user can use to make further API calls. When using a reverse proxy such as Apache in front of st2auth, those two CGI environment variables are usually set automatically by a proxy upon successful authentication. Auth BackendsThe service can be configured with different backends (i.e. PAM, LDAP, etc.) to handle the
authentication. If a backend is not specified, an htpasswd-compatible flat file authentication
backend is used. To use a different backend, select and install the appropriate python package from
the StackStorm community repos and configure
Note When using the For example, to install the package for the PAM backend manually, run the
following command on the same server where $ sudo /opt/stackstorm/st2/bin/pip install git+https://github.com/StackStorm/st2-auth-backend-pam.git@master#egg=st2_auth_backend_pam Note StackStorm uses a Python virtual environment in This means that if you want to work with the StackStorm installation (e.g. use the
You can do so by activating the virtual environment or running
# by activating the virtual environment

$ source /opt/stackstorm/st2/bin/activate

$ sudo pip install foo

# or by directly invoking binaries from the virtual environment
$ /opt/stackstorm/st2/bin/python

$ sudo /opt/stackstorm/st2/bin/pip install foo
After the backend is installed, configure the backend at [auth] mode = standalone backend = pam enable = True use_ssl = True cert = /path/to/ssl/cert/file key = /path/to/ssl/key/file logging = /etc/st2/logging.auth.conf api_url = https://myhost.examples.com/api/ debug = False The following is a list of auth backends for the community edition to help get things started: LDAPNote Prior to StackStorm 3.3, Extreme Networks provided a commercial version of the StackStorm automation platform which included LDAP auth backend. As these enterprise features were donated to the Linux Foundation, LDAP auth backend is now available in StackStorm Open Source since 3.4. LDAP is now included by default with StackStorm core and needs to be enabled and configured via The LDAP backend authenticates the user against an LDAP server. The following is a list of configuration options for the backend:
Note By default a logical The following is a sample auth section for the LDAP backend in the st2 config file: [auth] mode = standalone backend = ldap backend_kwargs = {"bind_dn": "CN=st2admin,ou=users,dc=example,dc=com", "bind_password": "foobar123", "base_ou": "dc=example,dc=com", "group_dns": ["CN=st2users,ou=groups,dc=example,dc=com", "CN=st2developers,ou=groups,dc=example,dc=com"], "host": "identity.example.com", "port": 636, "use_ssl": true, "cacert": "/path/to/cacert.pem"} enable = True use_ssl = True cert = /path/to/mycert.crt key = /path/to/mycert.key logging = /etc/st2/logging.auth.conf api_url = http://myhost.example.com:9101/ debug = False If your LDAP server uses a different name for the user ID attribute, you can simply specify the id_attr configuration option. [auth] mode = standalone backend = ldap backend_kwargs = {"bind_dn": "CN=st2admin,ou=users,dc=example,dc=com", "bind_password": "foobar123", "base_ou": "dc=example,dc=com", "id_attr": "username", "group_dns": ["CN=st2users,ou=groups,dc=example,dc=com", "CN=st2developers,ou=groups,dc=example,dc=com"], "host": "identity.example.com", "port": 636, "use_ssl": true, "cacert": "/path/to/cacert.pem"} enable = True use_ssl = True cert = /path/to/mycert.crt key = /path/to/mycert.key logging = /etc/st2/logging.auth.conf api_url = http://myhost.example.com:9101/ debug = False This will need customization for your environment - e.g. the LDAP server to bind to, and the Running the Service
The service can be started with one of the options below: # Individually sudo service st2auth start # Individually via st2ctl sudo st2ctl start st2auth # Collectively with other st2 components sudo st2ctl start # Using the launcher for debugging purposes sudo /usr/bin/st2auth --config-file /etc/st2/st2.conf TestingRun the following # If use_ssl is set to True, the following will fail because SSL is required. curl -X POST http://myhost.example.com/auth/v1/tokens # The following will fail with 401 unauthorized. Please note that this is executed with "-k" to skip SSL cert verification. curl -X POST -k https://myhost.example.com/auth/v1/tokens # The following will succeed and return a valid token. Please note that this is executed with "-k" to skip SSL cert verification. curl -X POST -k -u yourusername:'yourpassword' https://myhost.example.com/auth/v1/tokens # The following will verify the SSL cert, succeed, and return a valid token. curl -X POST --cacert /path/to/cacert.pem -u yourusername:'yourpassword' https://myhost.example.com/auth/v1/tokens UsageOnce authentication is enabled, API calls require a token to be passed via the headers. CLI calls
require the token to be included as a CLI argument or as an environment variable. Using To use the CLI, use the # without password st2 login yourusename Password: # with password st2 login yourusername -p 'yourpassword' # write password to config file st2 login -w yourusername -p 'yourpassword' Note If your password contains special characters such as If you need to acquire a token - for example to use with an API call, use the # with password st2 auth yourusername -p 'yourpassword' # without password st2 auth yourusename Password: The following is a sample API call via $ curl -H "X-Auth-Token: 4d76e023841a4a91a9c66aa4541156fe" https://myhost.example.com/api/v1/actions This is the CLI equivalent: # Include the token as command line argument. st2 action list -t 4d76e023841a4a91a9c66aa4541156fe # Or set the token as an environment variable. export ST2_AUTH_TOKEN=4d76e023841a4a91a9c66aa4541156fe st2 action list There may be use-cases where you want a token with a different TTL from the default. You can specify a TTL (in seconds) when you request a token. For example, to request a token that is valid for 10 minutes: # with TTL and password st2 auth yourusername -p 'yourpassword' -l 600 Note that if the TTL requested is greater than the configured maximum allowed TTL, you will get an error. If you don’t want to retrieve a new token and configure the environment variable every time you start a new shell session, you can put your StackStorm credentials in the CLI configuration file. Then the CLI will automatically authenticate, retrieve and cache the auth token for you. For information on how to do that, see the CLI configuration page. API KeysStackStorm also supports API keys. These differ from tokens in that they do not expire. This makes them suited for integrations with other applications, e.g. through webhooks. All API key management is currently available via the StackStorm CLI or API. To create an API key: st2 apikey create -k -m '{"used_by": "my integration"}' <API_KEY_VALUE> Note For security purposes the <API_KEY_VALUE> is only shown at create time. StackStorm itself does not store this API Key value in its database, only a one-way hash is stored. It is not possible to retrieve an API Key after creation. If the API Key is lost or not recorded at the time of creation, delete the API Key and create a new one. The optional The CLI for API keys also support If an API Key is disabled it will disallow access until that API key is enabled again. This is a good way to temporarily revoke access of an external service to StackStorm. API Key UsageAPI keys are designed for API access. As of now they cannot be used via clients like the UI and CLI. The following are sample API calls via $ curl -H "St2-Api-Key: <API-KEY-VALUE>" https://myhost.example.com/api/v1/actions $ curl https://myhost.example.com/api/v1/actions?st2-api-key=<API-KEY-VALUE> API Key MigrationAPI keys can be migrated from one StackStorm instance to another. This way external services that have already been configured with API Keys do not need to be updated with a new set of keys. Follow these steps to migrate:
Using Authentication Tokens or API Keys with the APITo authenticate against the StackStorm API, either an authentication token or an API key (but not both)
should be provided in the HTTP request headers. The headers are named If for some reason you can’t specify an auth token or API key in the headers (e.g. you are using a
third party service to integrate with StackStorm and this service doesn’t allow you to specify custom
headers), you can provide it as a query parameter named Note Keep in mind that using HTTP header is preferred since some web servers and third party services log query parameters which are sent with each request. This could lead to auth token / api key exposure and potentially pose a security risk. Here’s some examples of how to send authentication token and API key in the headers, and as a query
parameter using
| |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| You are visitor 01402503 — GeezerVison does not store the pages you look up. Best viewed with Netscape Navigator 4.7 or Internet Explorer 6 at 800×600. No cookies required. | |||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||